The scary part of all this is that the vulnerability in Modernizr is a well-known flaw, yet BA’s system had been waiting seven years for an update.
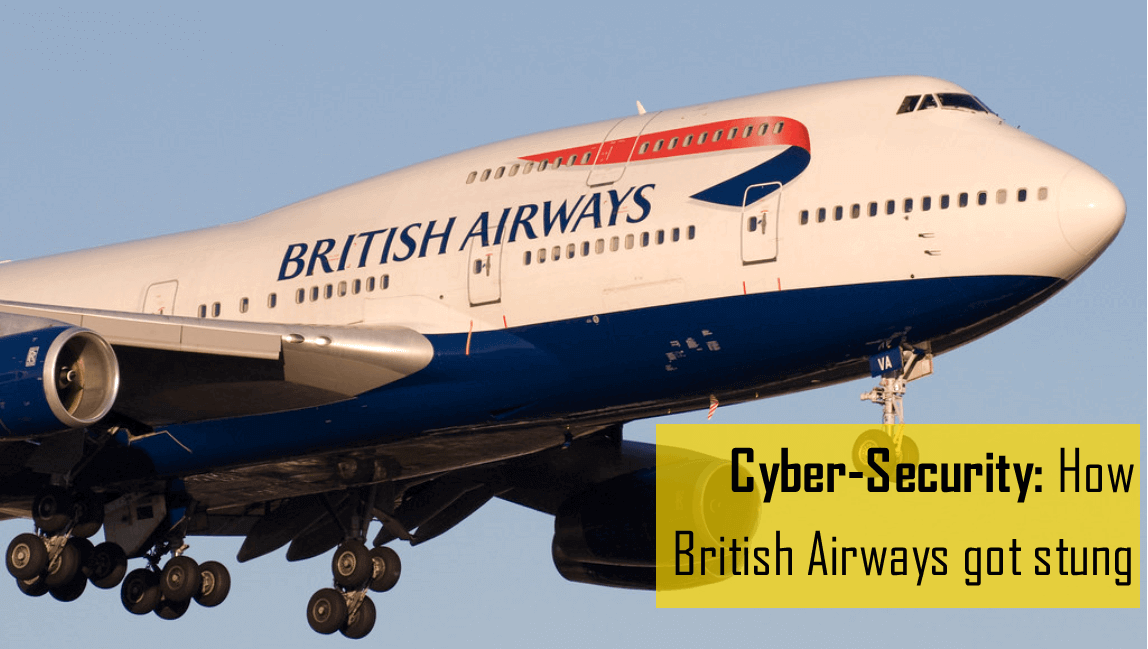
The ICO recently announced it was planning to fine the airline for a massive breach of customer data dating back to summer 2018, when users who booked flights through the BA app or website over the course of 12 weeks were directed to a fake website that filtered off their personal details, such as usernames & passwords, credit card details as well as important information required for travelling on flights, including names and addresses.
“The ICO fine shows how serious some of BA’s failings were with its payment processing both on its website and its app,” says Andrew Dwyer, a cybersecurity researcher at the University of Oxford.
Hackers accessed the information of an estimated half a million people, according to the ICO, through a vulnerability in third-party JavaScript used on the BA website, exploited by a hacking group called Magecart.
Magecart are believed to have secreted 22 lines of code that diverted crucial details around payments to a separate website controlled by the criminals. The third-party piece of JavaScript, Modernizr, sent data to baways.com – a similar-sounding website to the official one, but out of the control of the airline.
The scary part of all this is that the vulnerability in Modernizr is a well-known flaw, yet BA’s system had been waiting seven years for an update.
BA had according to WIRED magazine’s Christopher Stokel-Walker not updated this system since 2012, long after problems were known to exist.
“As a singular error it could be seen as fairly trivial – as it was one script that was compromised and used to exfiltrate data,” says Dwyer. “However, that it was not found for so long and that script had not been updated suggests a more systemic issue of IT governance at BA – meaning it is unlikely this is an isolated vulnerability. Effective monitoring would have picked up this quickly – not the three months it took BA.”
“Even today, its payment page still gives access to third-party scripts and does not add sufficient protections that would necessarily be expected to keep payment segmented from potential access from these third parties,” he adds.
This should come as a warning to businesses everywhere. The time of ignoring Data Protection and Cyber Security are well and truly over.